-
What Regulated Enterprises Can't Ignore
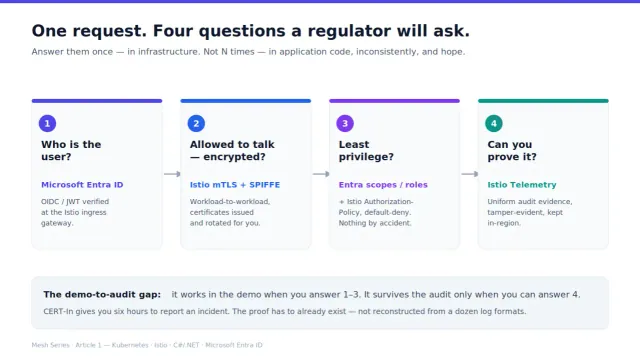
You're moving your web apps to Kubernetes. The kind of apps that ran happily on Windows servers for years. Back there, authentication was almost free. They sat inside the domain, Windows-integrated auth did the quiet work, LDAP…
-
What a Service Mesh Actually Does (and What It Doesn't)
A service mesh is a layer of proxies. That's the whole idea, stripped of the conference-stage mystique. Next to every pod, you run a second container — an Envoy proxy, the "sidecar" — and you route all of that pod's traffic…
-
Istio Without the Overwhelm
Istio has a reputation problem. You open the docs and drown: control planes, sidecars, gateways, virtual services, destination rules, telemetry pipelines, a CRD zoo that reads like someone was paid per resource kind. Most…
-
Microsoft Entra ID in plain language
You moved your web apps to Kubernetes and the authentication story fell apart on the way in.
Microsoft Entra ID.NET & C#Scopes & app rolesAzureKubernetes
-
The integration thesis — Entra for users, Istio for workloads
The most common identity mistake in a Kubernetes estate isn't a weak policy. It's a merged one.
-
Terminating user identity at the mesh edge
A bug that ships to production quietly, in regulated shops, all the time:
Microsoft Entra IDJWT validationOAuth 2.0 & OIDCAuthorizationPolicy.NET & C#
-
mTLS and SPIFFE — identity on the wire
Everyone claims they have mTLS. Almost nobody can prove it to an auditor. Those are two different jobs.
-
Default-deny — the AuthorizationPolicy that fails closed
In default-allow, a forgotten rule leaves a workload open — and you find out when infosec does, or an attacker does. In default-deny, a forgotten rule breaks a deployment in testing, in your face, where you fix it.
AuthorizationPolicyNetwork policyIstioMicrosoft Entra IDSPIFFE
-
Network policy and mesh policy — belt and suspenders
Your mesh AuthorizationPolicy has a blind spot: a pod without a sidecar. A DaemonSet, a node agent, a debug pod — it can open a raw socket to your ledger and the mesh never gets a vote, because the request never hit a proxy.
Network policyAuthorizationPolicyPolicy as codeSPIFFECompliance evidence
-
Egress control and the locked-down cluster
You locked the front door of your Kubernetes cluster. Ingress gateway, token validation, default-deny — the works.
-
If you can’t prove it, it didn’t happen — audit logging in the mesh
Your service mesh is already logging every request. Method, path, status code — for free.
-
Tracing identity through a request
You turned on distributed tracing. Grafana draws the pretty waterfall. You feel covered.
Distributed tracingLGTM stackCompliance evidenceIstioOpenTelemetry
-
The reference architecture — thirty-two pieces, one system
33 articles ago this series opened on a distributed monolith held together with auth tokens and prayer. This is where the pieces become one picture.
Ambient meshCompliance evidenceMicrosoft Entra IDAuthorizationPolicyPasswordless
-
DORA for platform engineers — what the Act actually asks of your cluster
You have spent thirty‑three articles building one system: a regulated .NET platform on AKS, Istio and Entra, where every request is authenticated, authorised, encrypted and logged, and where the logs are signed and the posture is…
-
NIS2 and the Austrian NISG 2026 — when the platform is the compliance measure and the board is on the hook
Last time you mapped DORA onto the cluster and drew one box with a dashed border: governance, owned by the management body, living in GRC rather than YAML. You treated that box as somebody else's problem.
-
Multi-cluster mesh for data residency — residency is a topology decision, not a config flag
Article 38 ended on a problem that sounds administrative and is not. Your Indian arm's CERT‑In report is due in six hours. The evidence that proves it — the access‑log lines, the signed aware‑at record, the Loki result set — must…
Multi-cluster & residencyCompliance evidenceSPIFFEAmbient meshIstio
-
Disaster recovery for a regulated mesh — recovering the proof, not just the app
A regional outage takes your primary cluster offline at 03:10. By 03:40 the platform team has a cluster in the paired region, Argo CD has reconciled the application manifests, and the dashboards are green. At 09:00 the ICT risk…
Compliance evidenceIstioDisaster recoveryGitOpsWorkload identity
-
Upgrading Istio without a control‑failure event — the traffic shift that is not a mutation
Istio 1.31.1 fixes GHSA‑qm8v‑g4f9‑qhjx: a BackendTLSPolicy that quietly reverts to plaintext when its CA reference fails to resolve. The control that encrypts was, under one specific failure, not encrypting. You read the advisory…