-
What Regulated Enterprises Can't Ignore
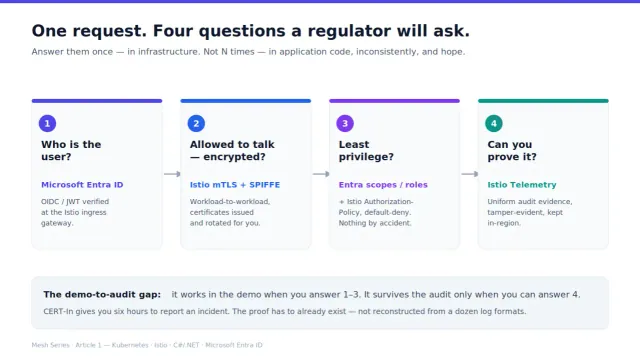
You're moving your web apps to Kubernetes. The kind of apps that ran happily on Windows servers for years. Back there, authentication was almost free. They sat inside the domain, Windows-integrated auth did the quiet work, LDAP…
-
What a Service Mesh Actually Does (and What It Doesn't)
A service mesh is a layer of proxies. That's the whole idea, stripped of the conference-stage mystique. Next to every pod, you run a second container — an Envoy proxy, the "sidecar" — and you route all of that pod's traffic…
-
Istio Without the Overwhelm
Istio has a reputation problem. You open the docs and drown: control planes, sidecars, gateways, virtual services, destination rules, telemetry pipelines, a CRD zoo that reads like someone was paid per resource kind. Most…
-
Going passwordless — for users and workloads
"Just add an OTP" is now the compliance answer that fails the audit.
-
The integration thesis — Entra for users, Istio for workloads
The most common identity mistake in a Kubernetes estate isn't a weak policy. It's a merged one.
-
Terminating user identity at the mesh edge
A bug that ships to production quietly, in regulated shops, all the time:
Microsoft Entra IDJWT validationOAuth 2.0 & OIDCAuthorizationPolicy.NET & C#
-
Defense in depth — validate at the mesh and in the code
If the gateway already validated the token, why validate it again in the service? Because no single control is the control — and the question that decides your architecture is which direction your mistakes fail.
-
mTLS and SPIFFE — identity on the wire
Everyone claims they have mTLS. Almost nobody can prove it to an auditor. Those are two different jobs.
-
Identity propagation across hops — keeping the user alive
Your service needs to call the next service on a user's behalf. The instinct — forward the user's token — is the confused-deputy bug.
On-behalf-of flowMicrosoft Entra IDScopes & app rolesWorkload identitymTLS
-
Threat-modelling a meshed .NET API
You've spent a dozen articles building controls. Now ask the question nobody budgets for: what does each one do when it BREAKS?
Threat modellingAuthorizationPolicyCompliance evidenceJWT validationCERT-In & DPDP
-
The LGTM stack for compliance evidence
Loki, Grafana, Tempo, Mimir. Four letters everyone treats as one observability blob. To a regulator they answer four different questions — and putting the wrong one in the wrong store is how evidence quietly disappears.
LGTM stackCompliance evidenceDistributed tracingMulti-cluster & residencyOpenTelemetry
-
Continuous posture and drift — proving the control is still holding
Your admission controller said yes to the policy six months ago. Is the policy still there?
Drift & posturePolicy as codeCompliance evidenceGitOpsLGTM stack
-
Mapping controls to frameworks — PCI-DSS 4.0 on the mesh
"Our service mesh makes us PCI compliant." If a vendor says that, end the meeting.
PCI DSSAuthorizationPolicyCompliance evidenceDrift & posturemTLS
-
Sidecar to ambient — what gets cheaper, what just moves house
"Sidecarless mesh, zero downtime" is a half-truth — and the missing half is exactly the one a regulated cluster cares about.
Ambient meshService meshMicrosoft Entra IDmTLSAuthorizationPolicy
-
The reference architecture — thirty-two pieces, one system
33 articles ago this series opened on a distributed monolith held together with auth tokens and prayer. This is where the pieces become one picture.
Ambient meshCompliance evidenceMicrosoft Entra IDAuthorizationPolicyPasswordless
-
NIS2 and the Austrian NISG 2026 — when the platform is the compliance measure and the board is on the hook
Last time you mapped DORA onto the cluster and drew one box with a dashed border: governance, owned by the management body, living in GRC rather than YAML. You treated that box as somebody else's problem.
-
Threat-led penetration testing under DORA — what the red team does once the mesh says yes
The letter from the supervisor is two paragraphs long. Your institution has been identified for threat-led penetration testing. A white team is to be formed. Scope will cover critical or important functions. Testing will run…
-
Multi-cluster mesh for data residency — residency is a topology decision, not a config flag
Article 38 ended on a problem that sounds administrative and is not. Your Indian arm's CERT‑In report is due in six hours. The evidence that proves it — the access‑log lines, the signed aware‑at record, the Loki result set — must…
Multi-cluster & residencyCompliance evidenceSPIFFEAmbient meshIstio
-
Disaster recovery for a regulated mesh — recovering the proof, not just the app
A regional outage takes your primary cluster offline at 03:10. By 03:40 the platform team has a cluster in the paired region, Argo CD has reconciled the application manifests, and the dashboards are green. At 09:00 the ICT risk…
Compliance evidenceIstioDisaster recoveryGitOpsWorkload identity